Lead with shared operating context, governed decisions, and evidence
Connect finance, legal, workforce, compliance, technology and operating priorities to the policies, authority, evidence and owners that determine what happens next.
A realistic coverage snapshot and multi-jurisdiction triage across policy, context and contiguous deployment.
| STATUS | OBJECT | FUNCTION | ENTITY | OWNER | DUE | ACTION |
|---|---|---|---|---|---|---|
| Authority required — within playbook | Capital asset deployment | Procurement | Vertix Global UK | CFO | 1st Aug | IN REVIEW |
| Evidence missing — further review | Executive appointment | Executive | Vertix Global UK | Legal Head | 1st Aug | IN REVIEW |
| 13 exceptions require sign-off | Product license agreement | Legal | Vertix Global UK | Chief Risk Officer | 28 Jul | OPEN (13) |
| Non-standard — owner unknown | Tax obligation inquiry | Tax | Northstar Singapore | Unassigned | 25 Jul | BLOCK |
| Readiness — preliminary only | International M&A | — | — | — | — | RESTRICTED |
Decisions, obligations and restrictions appear before any board meeting, no opaque global roll-up or summary replaces a single underlying journal record.
What does ZoikoSuite provide for leadership teams?
ZoikoSuite gives executive and control leaders a shared operating context in which business activity is connected to the policies and obligations that apply, the delegated authority required to act, the evidence that supports the decision, the accountable owner, and the state of the underlying source systems. It helps leadership teams see what needs a decision, why it matters, who may decide, and what the permitted next step is — across functions, entities, and jurisdictions.
Eight stages, one of which is always human
The same lifecycle applies whether the action originates in finance, legal, workforce, tax, compliance or procurement. Stage 06 cannot be automated away.
Propose
A change is initiated across human or system actor
Contextualize
Connecting jurisdiction, legal entity and policy context
Evaluate
Evaluating against policy and statutory obligations without exemption
Confirm authority
Verifying the authority boundary against the actor role
Assemble evidence
Compile evidence trail for external auditor / board inspection
Human decision
Accountable human commits the step with clear attribution
Enact across state
Propagating actions to internal systems and external gates
Preserve evidence
Preserving immutable records and downstream audit readiness
Everything needed to decide, in one record
This is the differentiating artifact. Not a notification and not a dashboard tile — a complete, attributable decision context that leaves no loose ends.
All supplier bank changes above £50k require 2-factor verified sign-off prior to transmission. 73-point checklist reference: PLY-BNK-MOD-01. Applicable version active from 12-Apr-2026.
Two independent verification calls required, currently zero recorded (dual-sign-off requirement unsatisfied).
- INVOICE:Verified PDF attached · 480KB · metadata matched · original invoice #88412
- REQUEST:Bank confirmed notification — received via Zendesk #91142
- RESEARCH:Supplier Intelligence Score — 91/100, no historic disputes
- WARNING:Recent SIM swap flag reported on account for finance director
ZoikoSuite has locked this record in SAP so it cannot be released automatically until this decision record is resolved.
All actions are recorded into the ZoikoSuite Immutable Journal. Timestamps are cryptographically sealed and cannot be altered.
What the board receives isn't a summary of someone's opinion on whether a supplier was paid. It is the real journal entry showing who approved it and under what authority, and how that decision was validated.
Your systems of record stay authoritative
Leadership teams rarely have the appetite to replace core systems in order to fix coordination. The decision packet above referenced four source systems and owned none of them.
- ―The policy evaluated and its evaluated outcome
- ―The authority and segregation check
- ―The evidence requirement and its proof
- ―The decision state and its evidence manifest
The supplier record, the invoice, the contract document and the payment execution path — each remained owned by its existing system.
| WHAT FAILS TODAY | HOW RESOLVED |
|---|---|
| Data in the report is from 4 different systems, no common timestamp or meaning | Shared identity, provenance, and canonical schema |
| Nobody can see who is permitted to approve a specific action | Delegated authority with scope, limit and delegation source |
| The report shows a sum, not an approval, and no trace of evidence | Separation evaluated before the decision is committed |
| Evidence is assembled in spreadsheets and emails when the audit arrives | Evidence reconstructed and locked while work proceeded |
| Actions happen in upstream systems without check | Forward policy gate placed on every item |
| Exceptions approved on email leave no audit trace | Exception recorded with compensating control and expiry |
Seven functions, one context model
A metric appears only where an approved source contract exists. Where today not, the function still appears — with that stated plainly rather than filled with a plausible number.
Finance
Workforce / People Ops
Employment contracts, IP assignment verification and cross-border right-to-work evidence recorded per jurisdictional node.
Legal & Governance
Entity records, Board resolutions, Articles of Association and statutory filings linked to operational decisions.
Tax
Clear attribution of tax nexus for intercompany charges, permanent establishment monitoring, and local statutory filings.
Compliance
Procurement & Commercial
Counterparty risk screening, MSA and DPA coverage, and invoice approval thresholds tied directly to legal terms.
Technology
Access rights, tenant data boundaries, software license compliance, and cryptographic integrity verification records.
Three groups, by what you are accountable for
No role is preselected. Nothing on this page infers your function from tracking or profile data — you choose where to start.
CFO
Balance sheet integrity, approval authority, backward payment context, no alter-native routes.
General Counsel
Contract obligations, legal review tracking, privilege boundaries, jurisdictional exposure.
CHRO
Workforce data borders, purpose-limited access, payroll release governance, no surveillance.
CIO
System ownership, integration health, coexistence with existing systems, deployment scope.
COO
Cross-functional throughput, bottlenecks, owner accountability, exception frequency.
Controller
Period-end and journal authority, reconciliation state, and evidence completeness.
Tax Leader
Obligation calendar, coverage status with source tables, and professional review routing.
Compliance Leader
Control outcomes, exception ownership, and auditor and regulator-ready evidence.
Audit Committee
Material exceptions, control provenance gaps, and traceability without operational access.
Board of Directors
Strategy and risk context, assurance posture, and entity-level exception concentration.
Read-only, and visibly so
An audit committee member should be able to trace a decision without holding any operational permission — and without the interface implying they could act.
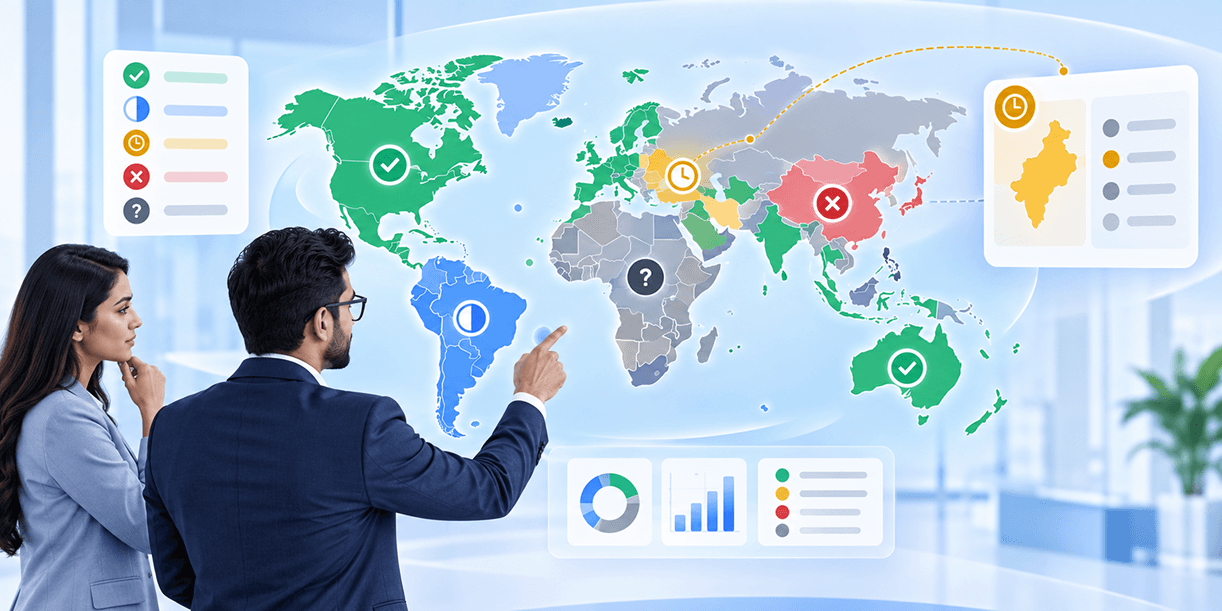
Six coverage states, never a green inference
Unknown, stale and partial states are explicit. A jurisdiction is never shown as covered because its neighbours are.
| JURISDICTION | STATUS | REGIME | EFFECTIVE | LAST REVIEWED | PROFESSIONAL REVIEW | EVIDENCE |
|---|---|---|---|---|---|---|
| United Kingdom | GOVERNED | Internal policy standard v4 | Apr 2026 | 22 Jul 2026 · Compliance | NOT REQUIRED | COMPLETE |
| Germany | PARTIAL | Statutory report v2 | Jan 2026 | 09 Jun 2026 · Tax Advisor | REQUIRED | DEFICIENT |
| India | REVIEW | Direct inquiry | Nov 2025 | 16 Feb 2026 · Unassigned | PENDING | OPEN |
| Singapore | CONFIGURATION REQUIRED | Local statute | Feb 2026 | 02 Jan 2026 · Tax Lead | NOT REQUIRED | PENDING |
| Brazil | NOT APPLICABLE | — | — | — | — | — |
A jurisdiction without a bar or state is not "in compliance". It is not tracked, and the interface is clear about it — so that no gap escapes governance notice. Explicit omission beats false reassurance.
Professional boundary. ZoikoSuite does not provide legal, tax, accounting, audit or regulatory advice, and does not guarantee compliance or any regulated outcome. Qualified professionals remain responsible for regulated judgment.
The brief and the decision stay separate
An executive brief can summarize. It cannot decide, and it never merges with the record of who did.
The brief can synthesize independent records into a single summary. It can flag gaps and highlight areas for review. It cannot write, certify or approve them — every figure it summarizes is directly traceable to the regulatory source. The brief may decrease risk; failure to separate it introduces a separate, actionable hazard.
Aggregate → entity → object → source
Every aggregate states its scope and denominator and drills to the records behind it, within permission. There is no opaque group-level record at any level.
| ENTITY | JURISDICTION | OPERATING STATUS | IN FORCE REGIMES | EXCEPTIONS | SIGNATURE READY | CURRENT AUDIT | DRILL |
|---|---|---|---|---|---|---|---|
| Northstar Holdings | United Kingdom | LIVE REGIME | 4 | 0 | 3 | EXEMPT | |
| Northstar UK Ltd | United Kingdom | LIVE REGIME | 4 | 2 | 2 | REVIEW (2) | |
| Northstar GmbH | Germany | LIVE REGIME | 4 | 0 | 1 | EXEMPT | |
| Northstar Singapore Pte Ltd | Singapore | LIVE REGIME | 2 | 0 | 0 | STALE | |
| David Holt (APAC) | Australia | — | — | — | — | UNRESOLVED |
Group-level reporting aggregate may look clean while an individual jurisdiction is stalled. ZoikoSuite preserves sovereign jurisdiction integrity.
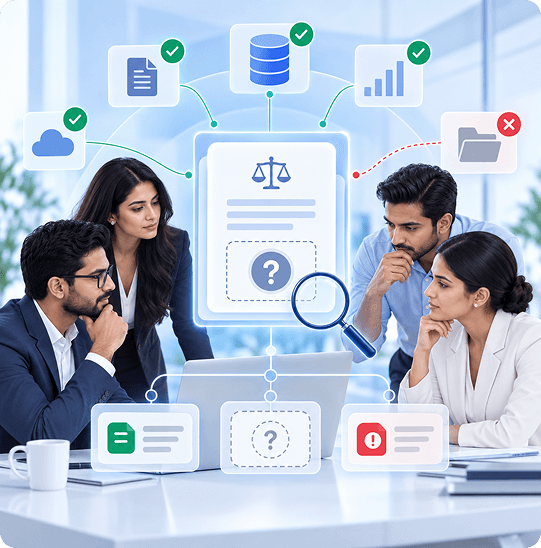
Diligence routes, and one deliberately empty block
Every provision above is synthetic. These are the routes where the claims get verified.
How the decision packet works
- ―Governance Platform
- ―Authority and segregation
- ―Documented lifecycle
What connects and who owns it
- ―Platform Foundation
- ―Deployment options
- ―Migration & Shadow Mode
Security and privacy
- ―Security overview
- ―Data Processing Agreement (DPA - Article 28)
- ―Subject requests
- ―Responsible AI
- ―Accessibility
Published resources only
Customer-case and evaluation material appears here only where an approved published resource exists. None is currently confirmed, so no eventuality allowed rather than a placeholder lien.
Evidence
- ―Evidence context model
- ―Evidence architecture
- ―Evidence health states
Professional boundary
No legal, tax, accounting, audit, employment or regulatory advice is provided, and no surveillance, certification or regulated outcome is guaranteed. Availability, coverage and integrations depend on approved scope and configuration.
No approved customer proofs published for this page
Named customers, outcomes, metrics and quotes appear only with documented permission covering the identity, the problem, the scope, the outcome, the measurement method and the period. Without that approval, this entry remains deliberately blank and filled with unsourced corporate hype.
Operational routes, no demo required
Reachable without a form
Bring one decision your team cannot currently evidence
The most realistic pilot for ZoikoSuite starts from a single real-life decision — one where nobody would want to acknowledge who made what under what authority, against which policy version, with what supporting evidence. We will walk that decision through the journal record with you.
An honest, 90-day pilot test is carefully structured with clear criteria and a plan for full institutional rollout.
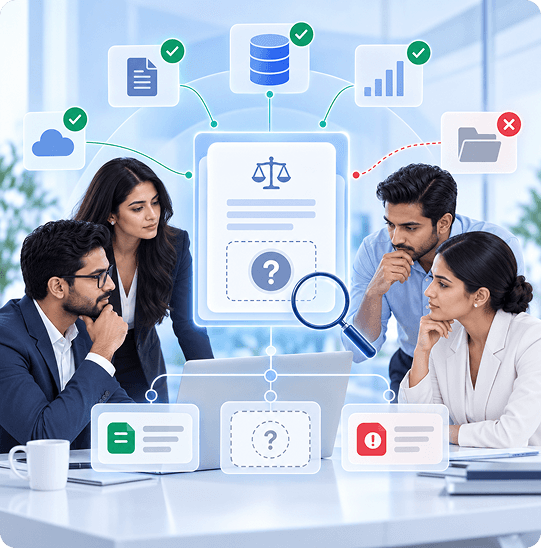
Authority, oversight, coexistence and boundaries
Three first sentences, manageable detail, 2-sec answers in plain English page section.
A dashboard tells you the status of something after the fact. It cannot tell you who approved what, under what authority, what policy applied, what evidence accompanied it, and whether the record can be altered. A dashboard shows you the weather; ZoikoSuite gives you the climate.
A single source of truth is not an improvement if it is not governed. Every record in ZoikoSuite has provenance: who created it, who signed it off, and who verified it is preserved.
Govern your global operations with confidence
Unify finance, workforce, legal, tax, compliance, and commercial operations under one governed platform.